Keeping keys
You type the key of a web service once, and it's there the next day, and the day after: in your persistent vault, a KeePass file that only your game can open with your password. The program creates the vault the first time, opens it on later days, keeps the key and shows its last four characters, so you can see which key it is without showing it.
Functions: HAS_VAULT, CREATE_VAULT, IS_VAULT_OPEN, OPEN_VAULT, SET_SECRET with persistent, HAS_SECRET, and RIGHT of c0de/strings
What you need
- an empty sheet, a SECRET block and a TAG block
- two trigger blocks with a button each, one for
storeand one forshow, and a laptop - a key or a code you want to keep – for a first try, any made-up text like
wx-3f9a-77c2-d00d
The idea
The vault of the door with a password forgets everything when you leave. That's fine for a password you choose each day, but not for a key that a web service gave you once, like the token of the home automation. For those, every player can have a persistent vault: a file in the KeePass format on the server, encrypted with a password that only you know.
The server keeps the file, but can't open it. Your game does the work:
- CREATE_VAULT asks you for a new password, makes an empty KeePass file in your game, encrypts it and sends it to the server.
- OPEN_VAULT asks for the password, gets the file from the server, decrypts it in your game and puts its secrets into your vault, where SECRET lines find them. It stays open until you leave.
- SET_SECRET with
persistentTRUE puts the secret into the vault and into the file: your game changes the file, encrypts it again and sends it back.
HAS_VAULT tells whether you have a file already, IS_VAULT_OPEN whether it's open. With these two, one function unlock does the right thing every time: nothing if the vault is open, OPEN_VAULT if there is a file, CREATE_VAULT if there isn't.
The program
PROGRAM keys
NOOP
INCLUDE c0de/security
INCLUDE c0de/strings
NOOP
CONSTANT NAME STRING "apiKey"
NOOP
FUNCTION unlock
    PARAMETER password STRING
    RESULT ready BOOLEAN
BEGIN
    VARIABLE exists BOOLEAN
    VARIABLE problem ERROR
    CALL c0de/security/IS_VAULT_OPEN
        RESULT result ready
    IF ready ;
    BEGIN
        RETURN
    END IF
    CALL c0de/security/HAS_VAULT
        RESULT result exists
    IF exists ;
    BEGIN
        CALL c0de/security/OPEN_VAULT problem
            PARAMETER password password ;
    END
    ELSE
    BEGIN
        CALL c0de/security/CREATE_VAULT problem
            PARAMETER password password ;
    END IF
    IF problem.code = VAULT_CANCELLED ;
    BEGIN
        CALL PRINT
            PARAMETER value "Cancelled. Your vault stays shut." ;
        RETURN
    END IF
    IF problem.code ≠ 0 ;
    BEGIN
        CALL PRINT
            PARAMETER value "? " ⊕ problem.message ;
        RETURN
    END IF
    IF NOT exists ;
    BEGIN
        CALL PRINT
            PARAMETER value "Your new vault is ready." ;
    END IF
    ASSIGN ready TRUE ;
END FUNCTION
NOOP
FUNCTION store
    PARAMETER password STRING ""
BEGIN
    VARIABLE ready BOOLEAN
    VARIABLE key STRING TAG(security: "sensitive")
    CALL CLS
    CALL unlock
        PARAMETER password password ;
        RESULT ready ready
    IF NOT ready ;
    BEGIN
        RETURN
    END IF
    CALL PRINT
        PARAMETER value "Key:" ;
    CALL INPUT
        PARAMETER variable key ;
        PARAMETER hide TRUE ;
    CALL c0de/security/SET_SECRET
        PARAMETER name NAME ;
        PARAMETER value key ;
        PARAMETER persistent TRUE ;
    CALL PRINT
        PARAMETER value "Key kept in your vault." ;
END FUNCTION
NOOP
FUNCTION peek
BEGIN
    SECRET apiKey STRING
    VARIABLE ending STRING
    CALL c0de/strings/RIGHT
        PARAMETER text apiKey ;
        PARAMETER length 4 ;
        RESULT result ending
    CALL PRINT
        PARAMETER value "Your key ends with ..." ⊕ ending ;
END FUNCTION
NOOP
FUNCTION show
    PARAMETER password STRING ""
BEGIN
    VARIABLE ready BOOLEAN
    VARIABLE known BOOLEAN
    CALL CLS
    CALL unlock
        PARAMETER password password ;
        RESULT ready ready
    IF NOT ready ;
    BEGIN
        RETURN
    END IF
    CALL c0de/security/HAS_SECRET
        PARAMETER name NAME ;
        RESULT result known
    IF NOT known ;
    BEGIN
        CALL PRINT
            PARAMETER value "No key in your vault. Run store first." ;
        RETURN
    END IF
    CALL peek
END FUNCTION
Building and running it
- Set the first trigger block to the program
keysand the functionstore, the second one toshow. Set Run to Only me on both: the vault only works for you anyway. Leave their input inventories empty – no item forpassword. - Bind the laptop to
keysandstore. - Press the button of
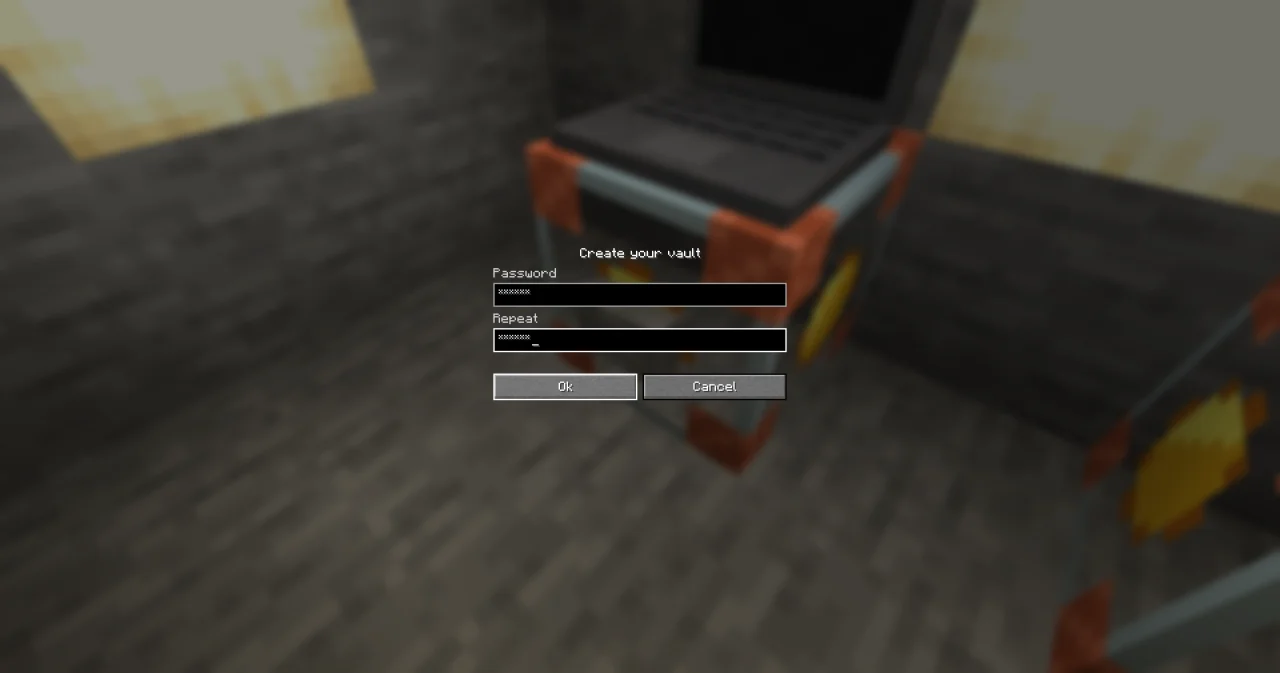
store. As you have no persistent vault yet, your game opens the dialog Create your vault with two fields, Password and Repeat. OK only works when both are the same. Choose a good password and remember it: nobody can open the vault without it, not even the administrator.
- The laptop shows
Your new vault is ready.andKey:. Type your key: the line shows a*for every character. After Enter, the cursor waits a moment while your game encrypts the file, and the laptop saysKey kept in your vault. - Bind the laptop to
keysandshow, and press the button ofshow. The vault is still open, so there's no dialog, and the laptop showsYour key ends with ...d00d.
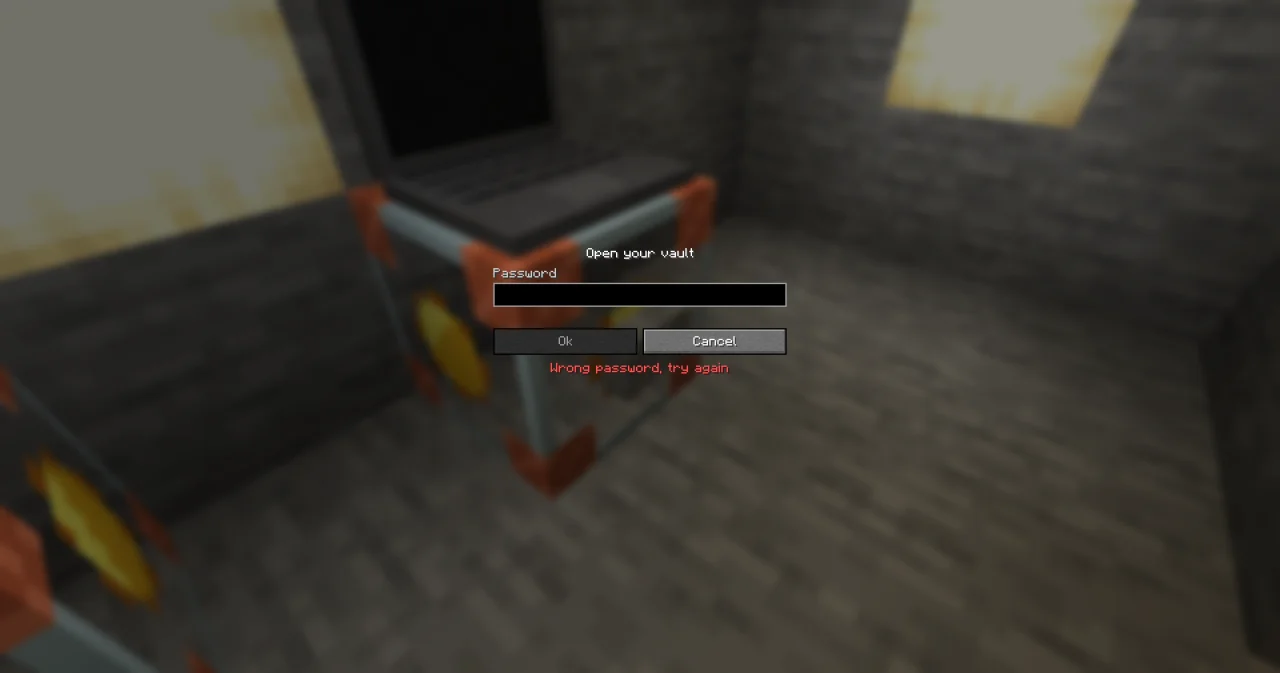
Now leave the server, join again and press the button of show. Your vault is closed, so the dialog Open your vault asks for the password. A wrong one gets Wrong password, try again in the dialog, which stays open. With the right one, the laptop shows the end of your key again. Cancel closes the dialog, and the laptop says Cancelled. Your vault stays shut.
Any program of yours can use the key now: open the vault, then SECRET apiKey STRING.
How it works
unlockdecides with IS_VAULT_OPEN and HAS_VAULT, which never ask anything. Only OPEN_VAULT and CREATE_VAULT open a dialog, and the cursor waits on their CALL line until you answer it. The error variableproblemcatches VAULT_CANCELLED for the Cancel button, and every other error (like WRONG_PASSWORD) with its message.- The parameter
passwordhas the default"", which means: ask the player. Leave it empty in the game – a password you type in the dialog never leaves your game. A password given as a parameter is sent from the server to your game, so the server sees it. That's how the program runner of the tests opens the vault: it has nobody to ask. If you ever pass the password as an item, make it a hidden item (Hide the value: "Yes, for good"). storereads the key with hidden INPUT intokey, which has the tagsecurity: "sensitive", and keeps it with SET_SECRET andpersistentTRUE. That needs an open vault – otherwise SET_SECRET raises VAULT_NOT_OPEN – whichunlocktook care of. A secondstorereplaces the key, in the vault and in the file.showasks HAS_SECRET first, because a SECRET line for a missing secret raises SECRET_NOT_FOUND.peekreads it and shows only the last four characters with RIGHT.
What the server sees – and what it doesn't
The server never sees:
- the password you type in the dialog: it stays in your game,
- what's in the file: it only stores it, encrypted, as
<world>/data/c0de_vaults/<your UUID>.kdbx.
The server sees:
- your secrets while the vault is open: they are in its memory, where SECRET lines read them,
- the key you type on the laptop: INPUT goes through the server,
- a password that a program passes to CREATE_VAULT or OPEN_VAULT.
So the persistent vault protects your keys on the disk of the server: in backups, copies of the world and while you are offline. While you play, the server holds them in memory, like every value a program uses. And administrators can change every sheet, also yours. Use the vault on servers whose administrators you trust.
The file is a normal KeePass database (KDBX 4): your secrets are entries of the group c0de, with the name as title and the value as password. With a copy of the file, KeePass and other password managers open it with your password.
Try it yourself
- Write a program that tells you about your vault without opening it: whether you have one, whether it's open, and whether the key is in your vault.
Solution
PROGRAM vaultstatus
NOOP
INCLUDE c0de/security
NOOP
FUNCTION status
BEGIN
    VARIABLE exists BOOLEAN
    VARIABLE open BOOLEAN
    VARIABLE known BOOLEAN
    CALL CLS
    CALL c0de/security/HAS_VAULT
        RESULT result exists
    CALL c0de/security/IS_VAULT_OPEN
        RESULT result open
    CALL c0de/security/HAS_SECRET
        PARAMETER name "apiKey" ;
        RESULT result known
    IF NOT exists ;
    BEGIN
        CALL PRINT
            PARAMETER value "Vault: none yet" ;
    END IF
    IF exists AND NOT open ;
    BEGIN
        CALL PRINT
            PARAMETER value "Vault: locked" ;
    END IF
    IF open ;
    BEGIN
        CALL PRINT
            PARAMETER value "Vault: open" ;
    END IF
    IF known ;
    BEGIN
        CALL PRINT
            PARAMETER value "Key: ready" ;
    END
    ELSE
    BEGIN
        CALL PRINT
            PARAMETER value "Key: not here" ;
    END IF
END FUNCTION
HAS_VAULT, IS_VAULT_OPEN and HAS_SECRET never ask for a password. A closed vault shows Vault: locked and Key: not here: the key is in the file, but not in your vault until OPEN_VAULT puts it there.
- Add a function
forgetthat removes the key for good, from the vault and from the file.
Solution
PROGRAM keysforget
NOOP
INCLUDE c0de/security
INCLUDE c0de/strings
NOOP
CONSTANT NAME STRING "apiKey"
NOOP
FUNCTION unlock
    PARAMETER password STRING
    RESULT ready BOOLEAN
BEGIN
    VARIABLE exists BOOLEAN
    VARIABLE problem ERROR
    CALL c0de/security/IS_VAULT_OPEN
        RESULT result ready
    IF ready ;
    BEGIN
        RETURN
    END IF
    CALL c0de/security/HAS_VAULT
        RESULT result exists
    IF exists ;
    BEGIN
        CALL c0de/security/OPEN_VAULT problem
            PARAMETER password password ;
    END
    ELSE
    BEGIN
        CALL c0de/security/CREATE_VAULT problem
            PARAMETER password password ;
    END IF
    IF problem.code = VAULT_CANCELLED ;
    BEGIN
        CALL PRINT
            PARAMETER value "Cancelled. Your vault stays shut." ;
        RETURN
    END IF
    IF problem.code ≠ 0 ;
    BEGIN
        CALL PRINT
            PARAMETER value "? " ⊕ problem.message ;
        RETURN
    END IF
    IF NOT exists ;
    BEGIN
        CALL PRINT
            PARAMETER value "Your new vault is ready." ;
    END IF
    ASSIGN ready TRUE ;
END FUNCTION
NOOP
FUNCTION store
    PARAMETER password STRING ""
BEGIN
    VARIABLE ready BOOLEAN
    VARIABLE key STRING TAG(security: "sensitive")
    CALL CLS
    CALL unlock
        PARAMETER password password ;
        RESULT ready ready
    IF NOT ready ;
    BEGIN
        RETURN
    END IF
    CALL PRINT
        PARAMETER value "Key:" ;
    CALL INPUT
        PARAMETER variable key ;
        PARAMETER hide TRUE ;
    CALL c0de/security/SET_SECRET
        PARAMETER name NAME ;
        PARAMETER value key ;
        PARAMETER persistent TRUE ;
    CALL PRINT
        PARAMETER value "Key kept in your vault." ;
END FUNCTION
NOOP
FUNCTION peek
BEGIN
    SECRET apiKey STRING
    VARIABLE ending STRING
    CALL c0de/strings/RIGHT
        PARAMETER text apiKey ;
        PARAMETER length 4 ;
        RESULT result ending
    CALL PRINT
        PARAMETER value "Your key ends with ..." ⊕ ending ;
END FUNCTION
NOOP
FUNCTION show
    PARAMETER password STRING ""
BEGIN
    VARIABLE ready BOOLEAN
    VARIABLE known BOOLEAN
    CALL CLS
    CALL unlock
        PARAMETER password password ;
        RESULT ready ready
    IF NOT ready ;
    BEGIN
        RETURN
    END IF
    CALL c0de/security/HAS_SECRET
        PARAMETER name NAME ;
        RESULT result known
    IF NOT known ;
    BEGIN
        CALL PRINT
            PARAMETER value "No key in your vault. Run store first." ;
        RETURN
    END IF
    CALL peek
END FUNCTION
NOOP
FUNCTION forget
    PARAMETER password STRING ""
BEGIN
    VARIABLE ready BOOLEAN
    VARIABLE problem ERROR
    CALL CLS
    CALL unlock
        PARAMETER password password ;
        RESULT ready ready
    IF NOT ready ;
    BEGIN
        RETURN
    END IF
    CALL c0de/security/DELETE_SECRET problem
        PARAMETER name NAME ;
    IF problem.code = SECRET_NOT_FOUND ;
    BEGIN
        CALL PRINT
            PARAMETER value "There is no key to forget." ;
        RETURN
    END IF
    CALL PRINT
        PARAMETER value "Key forgotten, also in the file." ;
END FUNCTION
DELETE_SECRET removes a persistent secret from the file too, and for that the vault must be open: so forget calls unlock first. A key that isn't there raises SECRET_NOT_FOUND, which problem catches.
Read more
- c0de/security: HAS_VAULT, CREATE_VAULT, IS_VAULT_OPEN, OPEN_VAULT, SET_SECRET, HAS_SECRET, DELETE_SECRET
- Secrets in the vault in the guide, SECRET in the handbook Data
- RIGHT of c0de/strings
- Hidden items in the handbook Tools
- A door with a password: the vault without a file